How does a NIS2 risk assessment with AI work?
A connected AI assistant adopts the BSI's method in item 2.1. In 2.3 it proposes frequency and damage for each program, each piece of technology and each supplier. You check every row. Management signs off in item 7.3, signed in with its own account; an assistant cannot.



What does the AI assistant do in the risk assessment?
An AI assistant connects to your company in the app through MCP (Model Context Protocol), an open standard. It fills in the NIS 2 walkthrough as the person who connected it, with that person's rights.
In 2.1, “Decide how you rate risks”, it can adopt the ready-made method from BSI Standard 200-3, just as you would with “Adopt”. The method has four levels for frequency, four for damage and four risk levels.
In 2.3, “Rate your risks”, it sets two values for each entry: how often the worst realistic case happens and how big the damage would be. If asked, it adds a note, for example what you already do about it.
The matrix turns that into a level: low, medium, high or very high. Until you have checked them and management signs off, these are proposals.
Art. 21(2)(a) NIS 2 · § 30(2) no. 1 BSIG
How does the assistant know your company's risks?
An assistant knows what your records say. That the inventory system went down twice last month, or that a supplier would be hard to replace, it knows only if someone wrote it down.
You bring that judgement. Think of fire, water and power cuts, and remember that rare does not mean small: in the BSI matrix, damage that threatens the company's existence is never low.
How do you check the assistant's proposals?
Check every row on the three screens “Rate your software”, “Rate your technology and rooms” and “Rate your suppliers”. Every screen an assistant wrote shows its name and the day.
The overview “Your risks at a glance” then shows how many entries sit in each field of the matrix. Below it, all of them are listed by name, highest level first.
You change a rating there by tapping the name or the field.
What does management do in item 7.3?
In 7.3, “Record the management review”, management sees the risk map on the screen “Your risks for management”: where your software, technology and suppliers stand today. It decides where to act first and records in “Your management review” what has to be done, by whom and by when.
Under “What the answers still leave open”, the walkthrough shows what is still missing by your own answers. Only fixed cases appear there by themselves, for example a supplier rated high or very high whose contract settles neither security nor incidents. Another is a backup with no restore that worked.
For each open point, you set in the app who takes care of it and by when. For its digital services, the Implementing Regulation requires identifying this for the risk treatment measures (Annex point 2.1.2(i)).
No assistant fills this part: the management review, the open points and the sign-off are done by a person in the app. Signing off is for whoever holds the management role in the app, signed in with their own account. Why the law leaves this decision with management is explained in our article on who answers for AI entries.
Art. 20(1) NIS 2 · § 38(1) BSIG
What happens when something changes after the sign-off?
If a person changes a rating in the app after the sign-off, item 2.3 goes back to management, because the sign-off was given on the old values. For a supplier this applies to 5.1 and 5.2 as well. Only sign-offs older than the change are taken back.
While an item that relies on the ratings or the supplier list is signed off, such as 2.3, 5.1 or 5.2, the tools refuse the assistant's rating. The refusal names the items.
The same goes for the method in 2.1, because adopting it replaces the scales the ratings sit on. Taking a sign-off back is a person's step: you make the change in the app, and the item goes to management again.
How the walkthrough does it
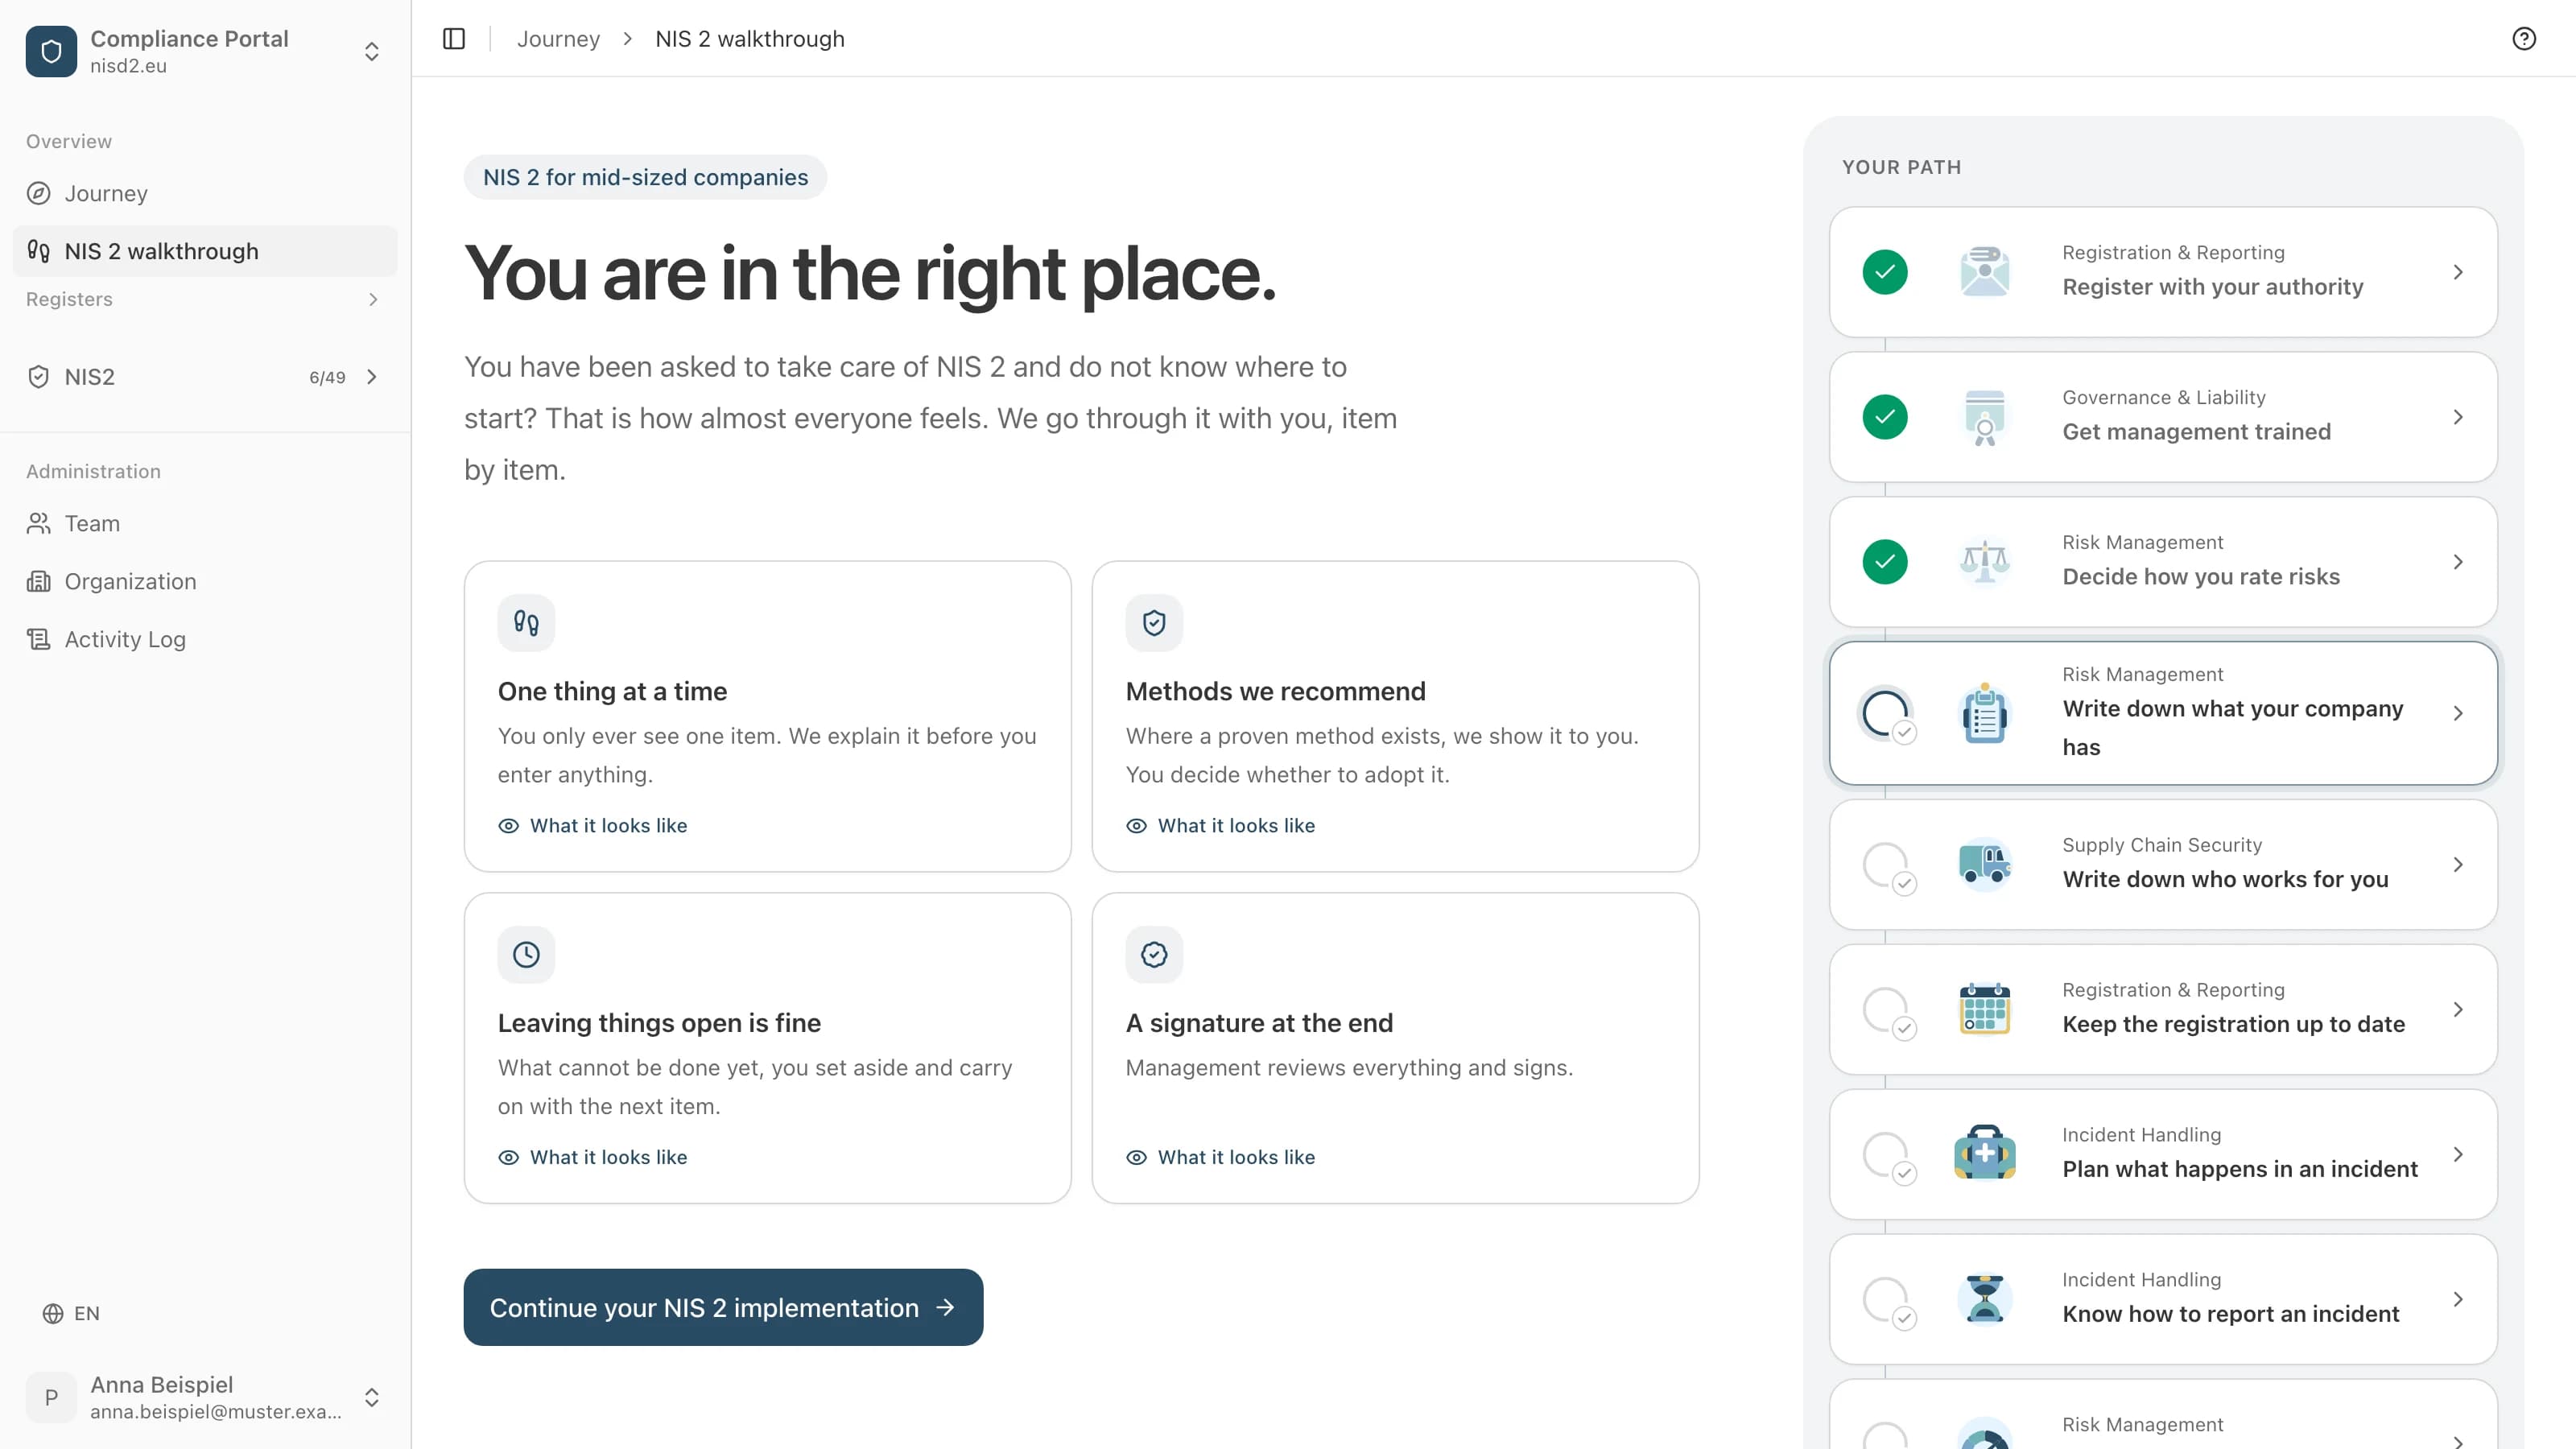
Rating is spread across three items of the walkthrough, and the last one belongs to management.
2.1, “Adopt the risk assessment method”: the assistant can adopt the method from BSI Standard 200-3. You read the matrix and finish 2.1.
2.3, “Rate your software”, “Rate your technology and rooms” and “Rate your suppliers”: it proposes frequency and damage for each entry. You check every row, change what does not fit and finish 2.3.
7.3, “Your risks for management” and “Your management review”: management sees the map, decides where to act first and records who does what by when.
7.3, “Management approves the documents”: you set who takes care of each open point and by when. Then management signs off, signed in with its own account. No tool of any assistant reaches this step.
Common questions
May AI do the NIS 2 risk analysis?
The NIS 2 directive and Implementing Regulation (EU) 2024/2690 say nothing about who or what prepares an assessment. They settle who approves and oversees: management. We have found no statement from the BSI, ENISA or any other authority on records an AI helped prepare.
Which risk assessment method does NIS 2 prescribe?
The law does not prescribe a particular method. In 2.1 the walkthrough offers the ready-made method from BSI Standard 200-3, which you or your assistant can adopt.
Who has to accept the residual risks?
Management approves the measures and oversees them (Art. 20(1) NIS 2, § 38(1) BSIG). For the regulation's digital services it is stated expressly that management accepts the results and residual risks, or an accountable person who reports adequately to it (Annex point 2.1.1). In the walkthrough, management signs off the ratings together with item 2.3 in 7.3.
Does every high risk become an open point by itself?
No. Only cases that follow from fixed answers appear there by themselves, for example a supplier rated high or very high whose contract settles neither security nor incidents. What happens about a program or device rated high, management decides when it sees the risk map in 7.3, and records it in its management review.
What happens if I change one of the assistant's ratings?
Before the sign-off, your change simply applies. The assistant's mark stays, so it remains visible that it entered data there. After the sign-off, 2.3 goes back to management with your change.
Read next
- How do I conduct a NIS 2 risk assessment?Step by step: asset scope, threat model, likelihood-impact, treatment plan, sign-off. What CIR §2 requires in practice.
- Who is liable for AI entries under NIS2?Art. 20 NIS 2 puts approval and oversight on management, whoever did the typing. Whose entry it is in the walkthrough, and why no assistant approves.
- Building an asset inventory for NIS2 with AIFrom an inventory, licence list or CMDB export, an AI assistant fills the lists in item 2.2. What belongs in it under NIS 2, and what you check yourself.
Sources
- Directive (EU) 2022/2555 (NIS 2), Art. 20(1) and Art. 21(2)(a), EUR-Lex
- BSIG, § 30(2) no. 1 and § 38(1), gesetze-im-internet.de
- Implementing Regulation (EU) 2024/2690, Annex points 2.1.1 and 2.1.2(i), EUR-Lex
- BSI, Standard 200-3: Risk Analysis based on IT-Grundschutz, bsi.bund.de
- open-isms, lib/compliance/module-recheck.ts (which sign-off a change takes back), lib/mcp/procedures.ts (what an assistant may call) and lib/durchgang/gaps.ts (what becomes an open point by itself), github.com/NISD2/open-isms
In practice
Where this comes up in the walkthrough
The walkthrough turns this into steps you fill in, with the law explained beside each one. Open a step to see its screen, filled in for a made-up company.
Risk Management
Decide how you rate risks
We recommend a ready-made risk assessment method.
Risk Management
Rate your risks
Place every piece of software, every device and every supplier on the matrix.
Effectiveness Assessment
Record the management review
Management checks whether the measures work and approves your documents.
What the walkthrough costs
€4,800 net a year, plus VAT
30 days money backBy invoice, due in 30 days. Cancel within the first 30 days, before the first export or sign-off: invoice cancelled or money back.
Guided NIS 2 implementation, step by step
A history of changes and sign-offs to show your regulator
Deadlines and reminders for each requirement
Security questionnaire for your suppliers
Export to PDF or CSV at any time
Been asked to handle NIS2?
In the end you have everything in one document: what is done, what is still open, and your management's approval with name and date. The app writes the texts.