Supplier portal
One security questionnaire for all your customers.
Your customers fall under NIS 2 and have to check how securely their suppliers work. So they send you security questionnaires, each one in a different format. Here you answer the questions once and release them to every customer who invites you. Open Source, no lock-in.
Does your own company fall under NIS 2? Check applicability.
NIS 2 Directive (EU) 2022/2555 · CIR 2024/2690 · ENISA TIG v1.0
How it works
1Create the profile
Sign in, enter your company name and domain. The profile belongs to you, not to one of your customers.
2Answer once
Up to 50 questions on commitments, security management, incident plans and access; you only see the ones that fit what you deliver. Every question names the provision it rests on. Drafts are saved as you go.
3Invite customers
Each customer gets their own private link. They see your profile, the systems you run for them, and your certificates. They do not need an account.
4Report incidents
If a customer's system is affected, you report it from inside the portal. Only that one customer sees the report. It helps them with their duty under Art. 21(2)(d) NIS2 to keep the security of their supply chain in view.
What gets asked
The questions rest on Art. 21 NIS2, Implementing Regulation (EU) 2024/2690 and ENISA's Technical Implementation Guidance v1.0 from June 2025; each names the provision it rests on and, where one applies, the matching ISO 27001 control. It asks what a customer needs for their supply chain, and no more. The question set is public on GitHub.
nis2-supply-chain-questionnaire-schema- Identity and contact
- Legal name, address, domain, and who a customer reaches when something goes wrong. Plus the window you commit to responding in.
- Security practice
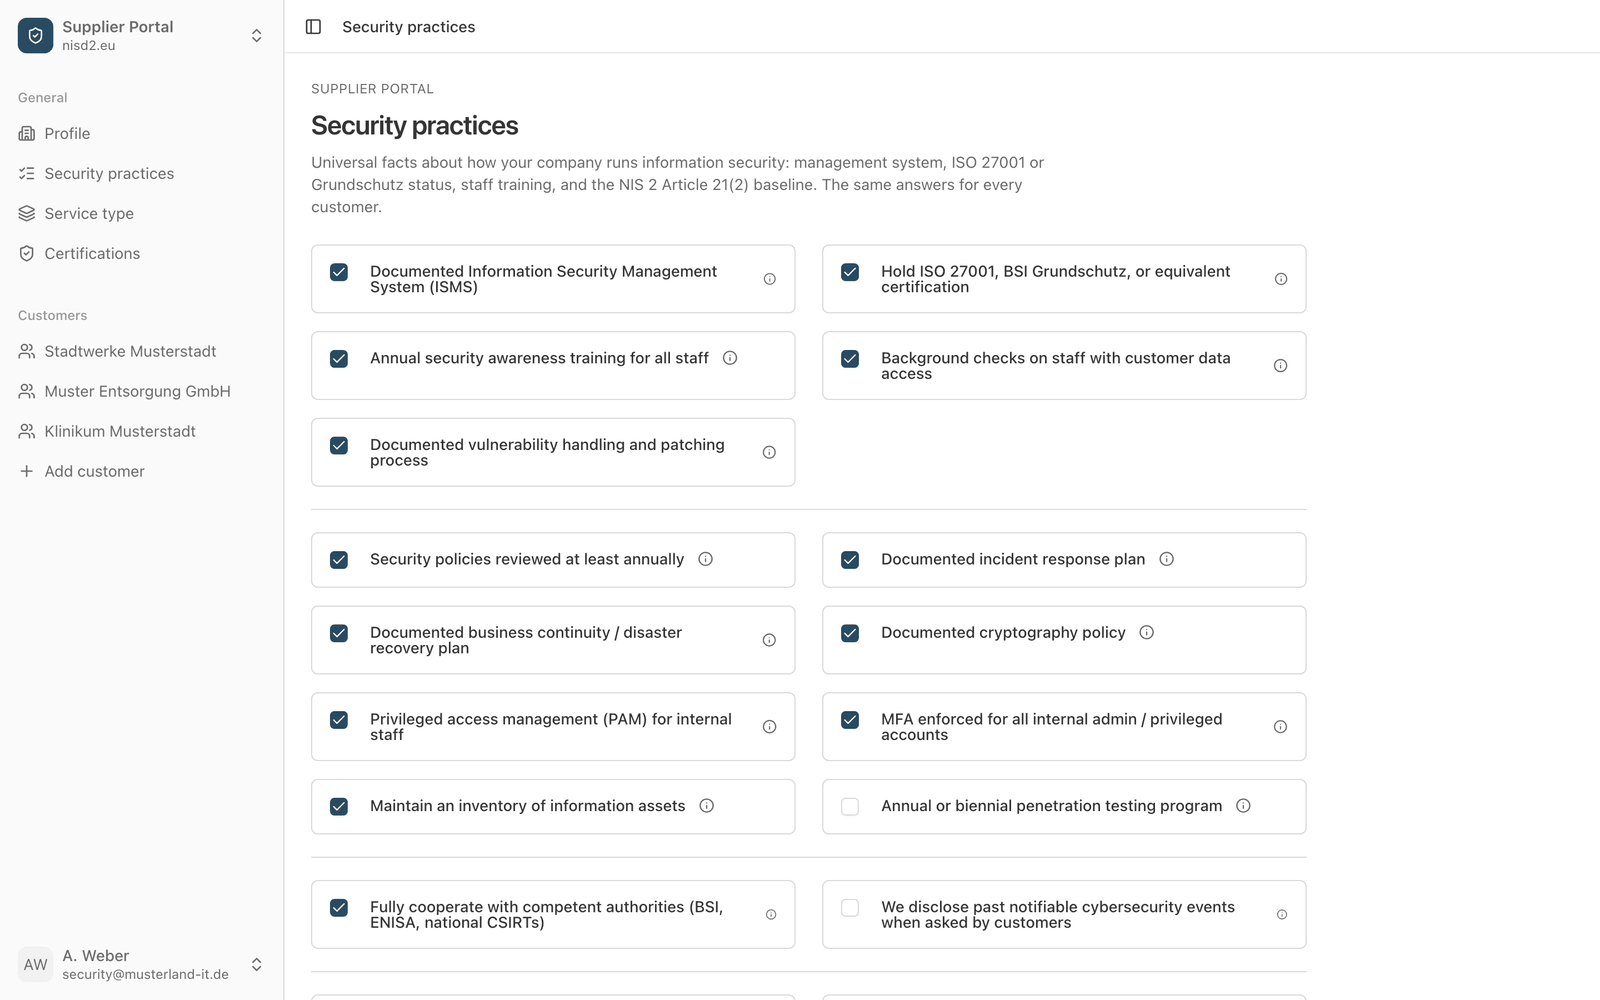
- How your company runs information security: management system, certification, training, vulnerability handling, access, continuity planning.
- Contract terms
- Right to audit, data processing agreement, subcontractors, confidentiality, hand-back at the end of the contract, notification of material changes.
- What you reach at customers
- Whether you hold your customers' data, reach their systems, enter their premises or deliver software. A tax adviser, a cleaning company and a software house each see only the questions that fit them.
- Certificates
- Upload ISO 27001, BSI C5, TISAX, SOC 2 or an equivalent as a PDF. Customers see how long it stays valid.
Bilateral and private
There is no public supplier directory. Only the customers you release it to can see your profile, and each of them can end their own access. No public address, no search engine indexing.
„Wir begrüßen aktuelle Vorstöße der Wirtschaft, einen einheitlichen Fragenkatalog für Lieferanten zu erarbeiten."
We welcome current industry initiatives to develop a unified question set for suppliers.
Why free?
The supplier portal costs nothing and the code is open. We earn from the guided walkthrough for companies under NIS 2, not from your data. Platform and question set are on GitHub, so you can check for yourself.
Ready in two minutes.
Sign in, enter your company name and domain, work through the questionnaire at your own pace. When you are ready, invite your customers.
Create supplier profile