Do NIS2 records filled in by AI hold up in an audit?
No authority has ruled on this so far, as far as we could check (as of October 2026). NIS 2 does not ask who typed a text. Supervisors can ask for evidence that your measures are implemented. So what they can check is whether your records describe what your company does, and whether management approved the measures.

Has any authority allowed or rejected NIS 2 records written by AI?
No, as far as we could check (as of October 2026). We found no statement from the BSI, ENISA or national authorities on whether records written by AI count.
The legal texts do not settle it either. NIS 2 mentions AI only in two recitals, Implementing Regulation (EU) 2024/2690 not at all. What they require is measures (Art. 21 NIS 2) and their approval by management (Art. 20(1)).
The German BSIG expressly requires companies to document how they comply with their duty to take risk management measures (§ 30(1) sentence 3 BSIG). None of these provisions says who has to type the document.
Art. 20(1) and Art. 21 NIS 2 · § 30(1) sentence 3 BSIG
What can supervisors ask for in an audit?
For essential entities, the authority may, among other things, carry out on-site inspections and regular and targeted security audits by an independent body or by the authority itself. It can request information, including your documented policies, and evidence of their implementation (Art. 32(2) NIS 2).
For important entities, the authority acts after the fact, when it has evidence, indications or information that an entity allegedly does not comply with NIS 2 (Art. 33(1)). It then has similar means, without regular audits.
In Germany, § 61 BSIG covers particularly important entities and § 62 BSIG important ones. In a review, a particularly important entity hands over the relevant records, documents and other papers on request (§ 61(5)). For an important entity, the BSI can take the same measures where facts suggest it does not implement its duties, or not correctly (§ 62). Operators of critical facilities prove implementation every three years through security audits, examinations or certifications (§ 39 BSIG).
Art. 32 and 33 NIS 2 · §§ 39, 61 and 62 BSIG
What matters for records an AI filled in?
That they are true. Supervisors can ask for evidence that your policies are implemented (Art. 32(2)(g) and Art. 33(2)(f) NIS 2). A policy describing measures your company does not have does not help with that.
ComplianceForge, a seller of documentation templates and so not neutral, writes from practice: “Auditors don't just review documentation, they compare it to reality.” In other words, auditors hold the records up against what actually happens in the company.
A language model can invent details that sound plausible: a backup schedule that never existed, or a second factor that is not switched on. So the walkthrough's server instructs the assistant to enter only what your documents and systems show, and to leave a field empty rather than guess. That instruction does not guarantee the model follows it.
Art. 32(2)(g) · Art. 33(2)(f) NIS 2
What does the walkthrough show an auditor?
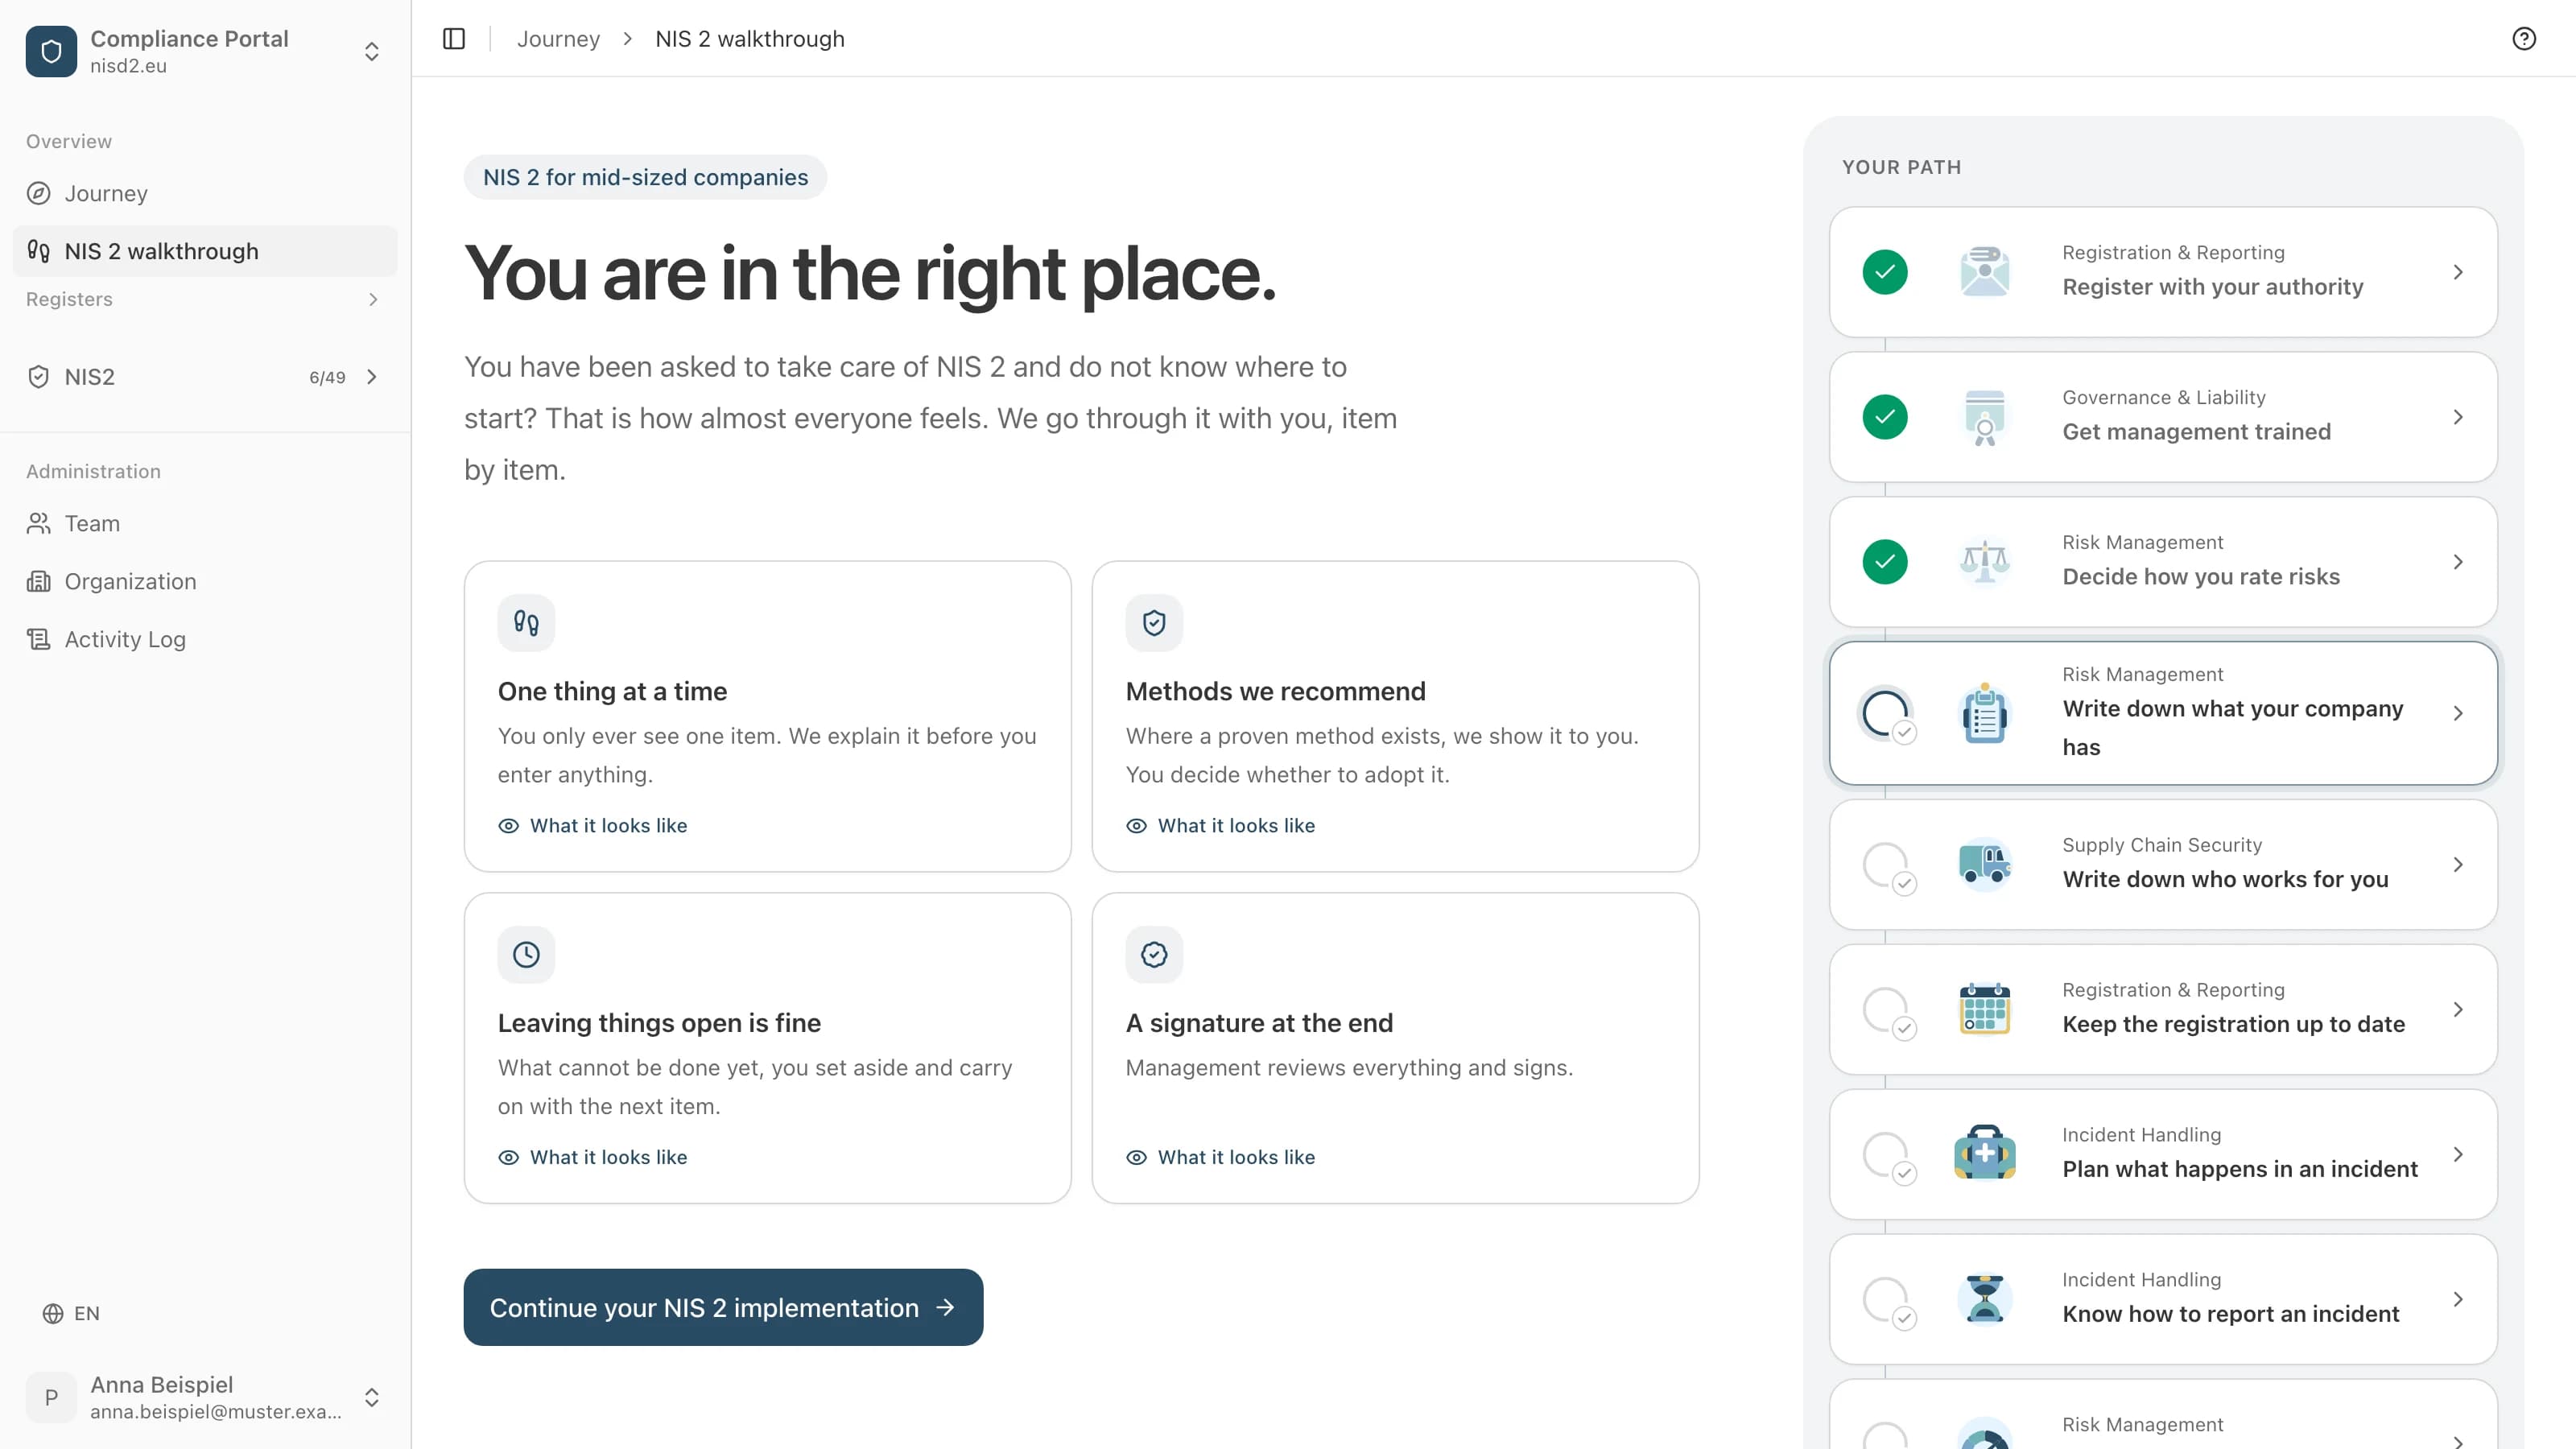
Every change appears in the activity log under the name of the person who made it. If it came through an assistant, it reads “via” and the assistant's name. Every screen an assistant wrote also carries a mark, for example “Filled in by the assistant claude-code/2.1.287 on 16 October 2026”.
Only a person can finish an item; no assistant can. In 7.3 management approves the documents, signed in with its own account. Each document then reads “Approved on” with the date and the name. For each open point, the screen records who takes care of it and by when.
The export “Everything in one document” sums up the whole walkthrough: status, open points, documents, risk matrix and all registers, each requirement with its approval. Admins, reviewers and management can export. The export does not show which entries came from an assistant; the mark in the app and the activity log show that.
How the walkthrough does it
Before an audit, four places in the walkthrough matter.
Screens with an assistant's mark: read these first, and check especially what only someone in the company can know, for example when a backup was last restored (4.4).
The activity log in the left sidebar under Administration: admins and people with the reviewer or legal reviewer role see which changes came through an assistant and who changed anything afterwards.
7.3 “Record the management review”: management sees the open points, each gets a person and a date, and management approves the documents. An assistant fills in nothing in 7.3.
12.4 “Detect attacks and prove it to the BSI”, only for operators of critical facilities: an assistant can enter the attack detection system and the day of the last evidence. The audit itself happens outside the walkthrough.
Common questions
Do I have to disclose that an AI wrote the records?
We found no such duty in NIS 2 or the BSIG. The AI Act requires deployers to disclose AI-generated text published to inform the public on matters of public interest (Art. 50(4)); on our reading, internal records are not that. In the walkthrough it is visible anyway, through the mark and the log.
Will an auditor accept AI-generated policies?
We cannot predict that, and we know of no rule on it. What can be asked for is evidence that a policy is implemented. In the walkthrough, a document goes further only once a person has ticked “I have read the document, and it fits our company”.
How often is a company audited under NIS 2?
NIS 2 sets no fixed interval for everyone. For essential entities regular and targeted audits are possible; for important ones the authority acts after the fact. In Germany the BSI can order individual particularly important entities to have audits by independent bodies (§ 61(1) BSIG) and ask other particularly important entities for evidence at the earliest three years after the law entered into force (§ 61(3)). Operators of critical facilities give evidence every three years (§ 39).
Does an auditor see in the export what the assistant entered?
No. The export shows status, documents, registers and approvals with names and dates. Which entries came from an assistant is shown by the mark on the screen and the activity log. In the app, admins and people with the reviewer or legal reviewer role see the log.
Read next
- Tracing AI entries: the audit trailEvery screen an assistant wrote carries its name and the day. Every change is in the log under the person, via the assistant.
- Who is liable for AI entries under NIS2?Art. 20 NIS 2 puts approval and oversight on management, whoever did the typing. Whose entry it is in the walkthrough, and why no assistant approves.
- How do I prepare for a BSI audit?Which evidence the BSI asks for, in what order, with what documentation depth. What has to be ready before the audit.
Sources
- Directive (EU) 2022/2555 (NIS 2), Art. 20, 21, 32 and 33, EUR-Lex, CELEX 32022L2555
- BSIG, § 30(1), § 39, § 61 and § 62, gesetze-im-internet.de
- Regulation (EU) 2024/1689 (AI Act), Art. 50(4), EUR-Lex, CELEX 32024R1689
- ComplianceForge, Can I pass an audit with AI generated documentation?, 18 June 2025, complianceforge.com (a seller of documentation templates)
- open-isms, lib/mcp/fills.ts, lib/mcp/agent.ts, lib/mcp/server.ts, lib/durchgang/gaps.ts, lib/export/access.ts and lib/export/company-export.ts, github.com/NISD2/open-isms
In practice
Where this comes up in the walkthrough
The walkthrough turns this into steps you fill in, with the law explained beside each one. Open a step to see its screen, filled in for a made-up company.
Effectiveness Assessment
Record the management review
Management checks whether the measures work and approves your documents.
Registration & Reporting
Detect attacks and prove it to the BSI
Operators of critical facilities only: attack detection and the evidence every three years.
What the walkthrough costs
€4,800 net a year, plus VAT
30 days money backBy invoice, due in 30 days. Cancel within the first 30 days, before the first export or sign-off: invoice cancelled or money back.
Guided NIS 2 implementation, step by step
A history of changes and sign-offs to show your regulator
Deadlines and reminders for each requirement
Security questionnaire for your suppliers
Export to PDF or CSV at any time
Been asked to handle NIS2?
In the end you have everything in one document: what is done, what is still open, and your management's approval with name and date. The app writes the texts.