NIS 2 consultant, or do it in-house?
The first question once NIS 2 lands on your desk. This page sets out what stays with you either way, what a consultant delivers and costs, and when a consultant is the better choice. We sell software for doing it in-house and earn on referrals to consultants. Both are disclosed below.

Implementing and overseeing
Management must implement the risk management measures and oversee their implementation (§ 38(1) BSIG, Art. 20(1) NIS 2). The law puts this duty on management, not on a service provider.
Management training
Management must attend training regularly itself (§ 38(3) BSIG, Art. 20(2) NIS 2). A consultant can run the training; management has to attend it.
Knowing your own operation
Which systems you run, which suppliers you depend on, who decides in an emergency: a consultant asks. The answers come from your company either way.
Running it afterwards
Reporting significant incidents (§ 32 BSIG, Art. 23 NIS 2) and keeping the measures current. That does not end with the project. Decide beforehand who does it afterwards.
What a consultant delivers, and what it costs
The usual entry point is a gap assessment: it shows what is missing. German consultancies publish prices between €2,000 and €6,900 for one, one-off and mostly as starting prices (cyberkom, ing-ism, Blackfort, DATAGROUP, and secunet, as of October 2026).
For the implementation afterwards we found no published prices that can be compared, so we name no number here.
What a good consultant brings: experience from other companies in your sector, an outside view of blind spots, and someone beside you when an auditor or a large customer asks questions.
Nobody in-house has the time
If no one can free up a few hours a week for NIS 2, the best software will not help. You need someone who does the work.
You want ISO 27001 certification
The certificate is issued by an accredited certification body. For the preparation, someone who has been through exactly this audit many times is worth it.
Plants and control systems
Securing grid control, production plants or medical technology takes expertise in exactly those systems. No software replaces it.
An incident is already under way
During a live security incident you need someone who can step in immediately. There are specialist incident response providers for that.
One person knows your IT
Someone in-house knows the systems and can work through it step by step, alongside the day job.
Your operation is manageable
A handful of core systems, known suppliers, clear responsibilities. Then many questions are answered quickly.
You want to keep the records yourself
A consultant's result is, in the end, your documentation too. The difference is who writes the reasons and what it costs. Whoever writes them can also keep them current.
The law measures against your company
Proportionality takes into account, among other things, the degree of risk exposure, the size of the entity and the cost of implementation (§ 30(1) sentence 2 BSIG, Art. 21(1) NIS 2). The effort follows your operation.
Something in between works too
You implement it yourself and bring in a consultant for individual points: the risk analysis of your control systems, a look before an audit, or the management training.
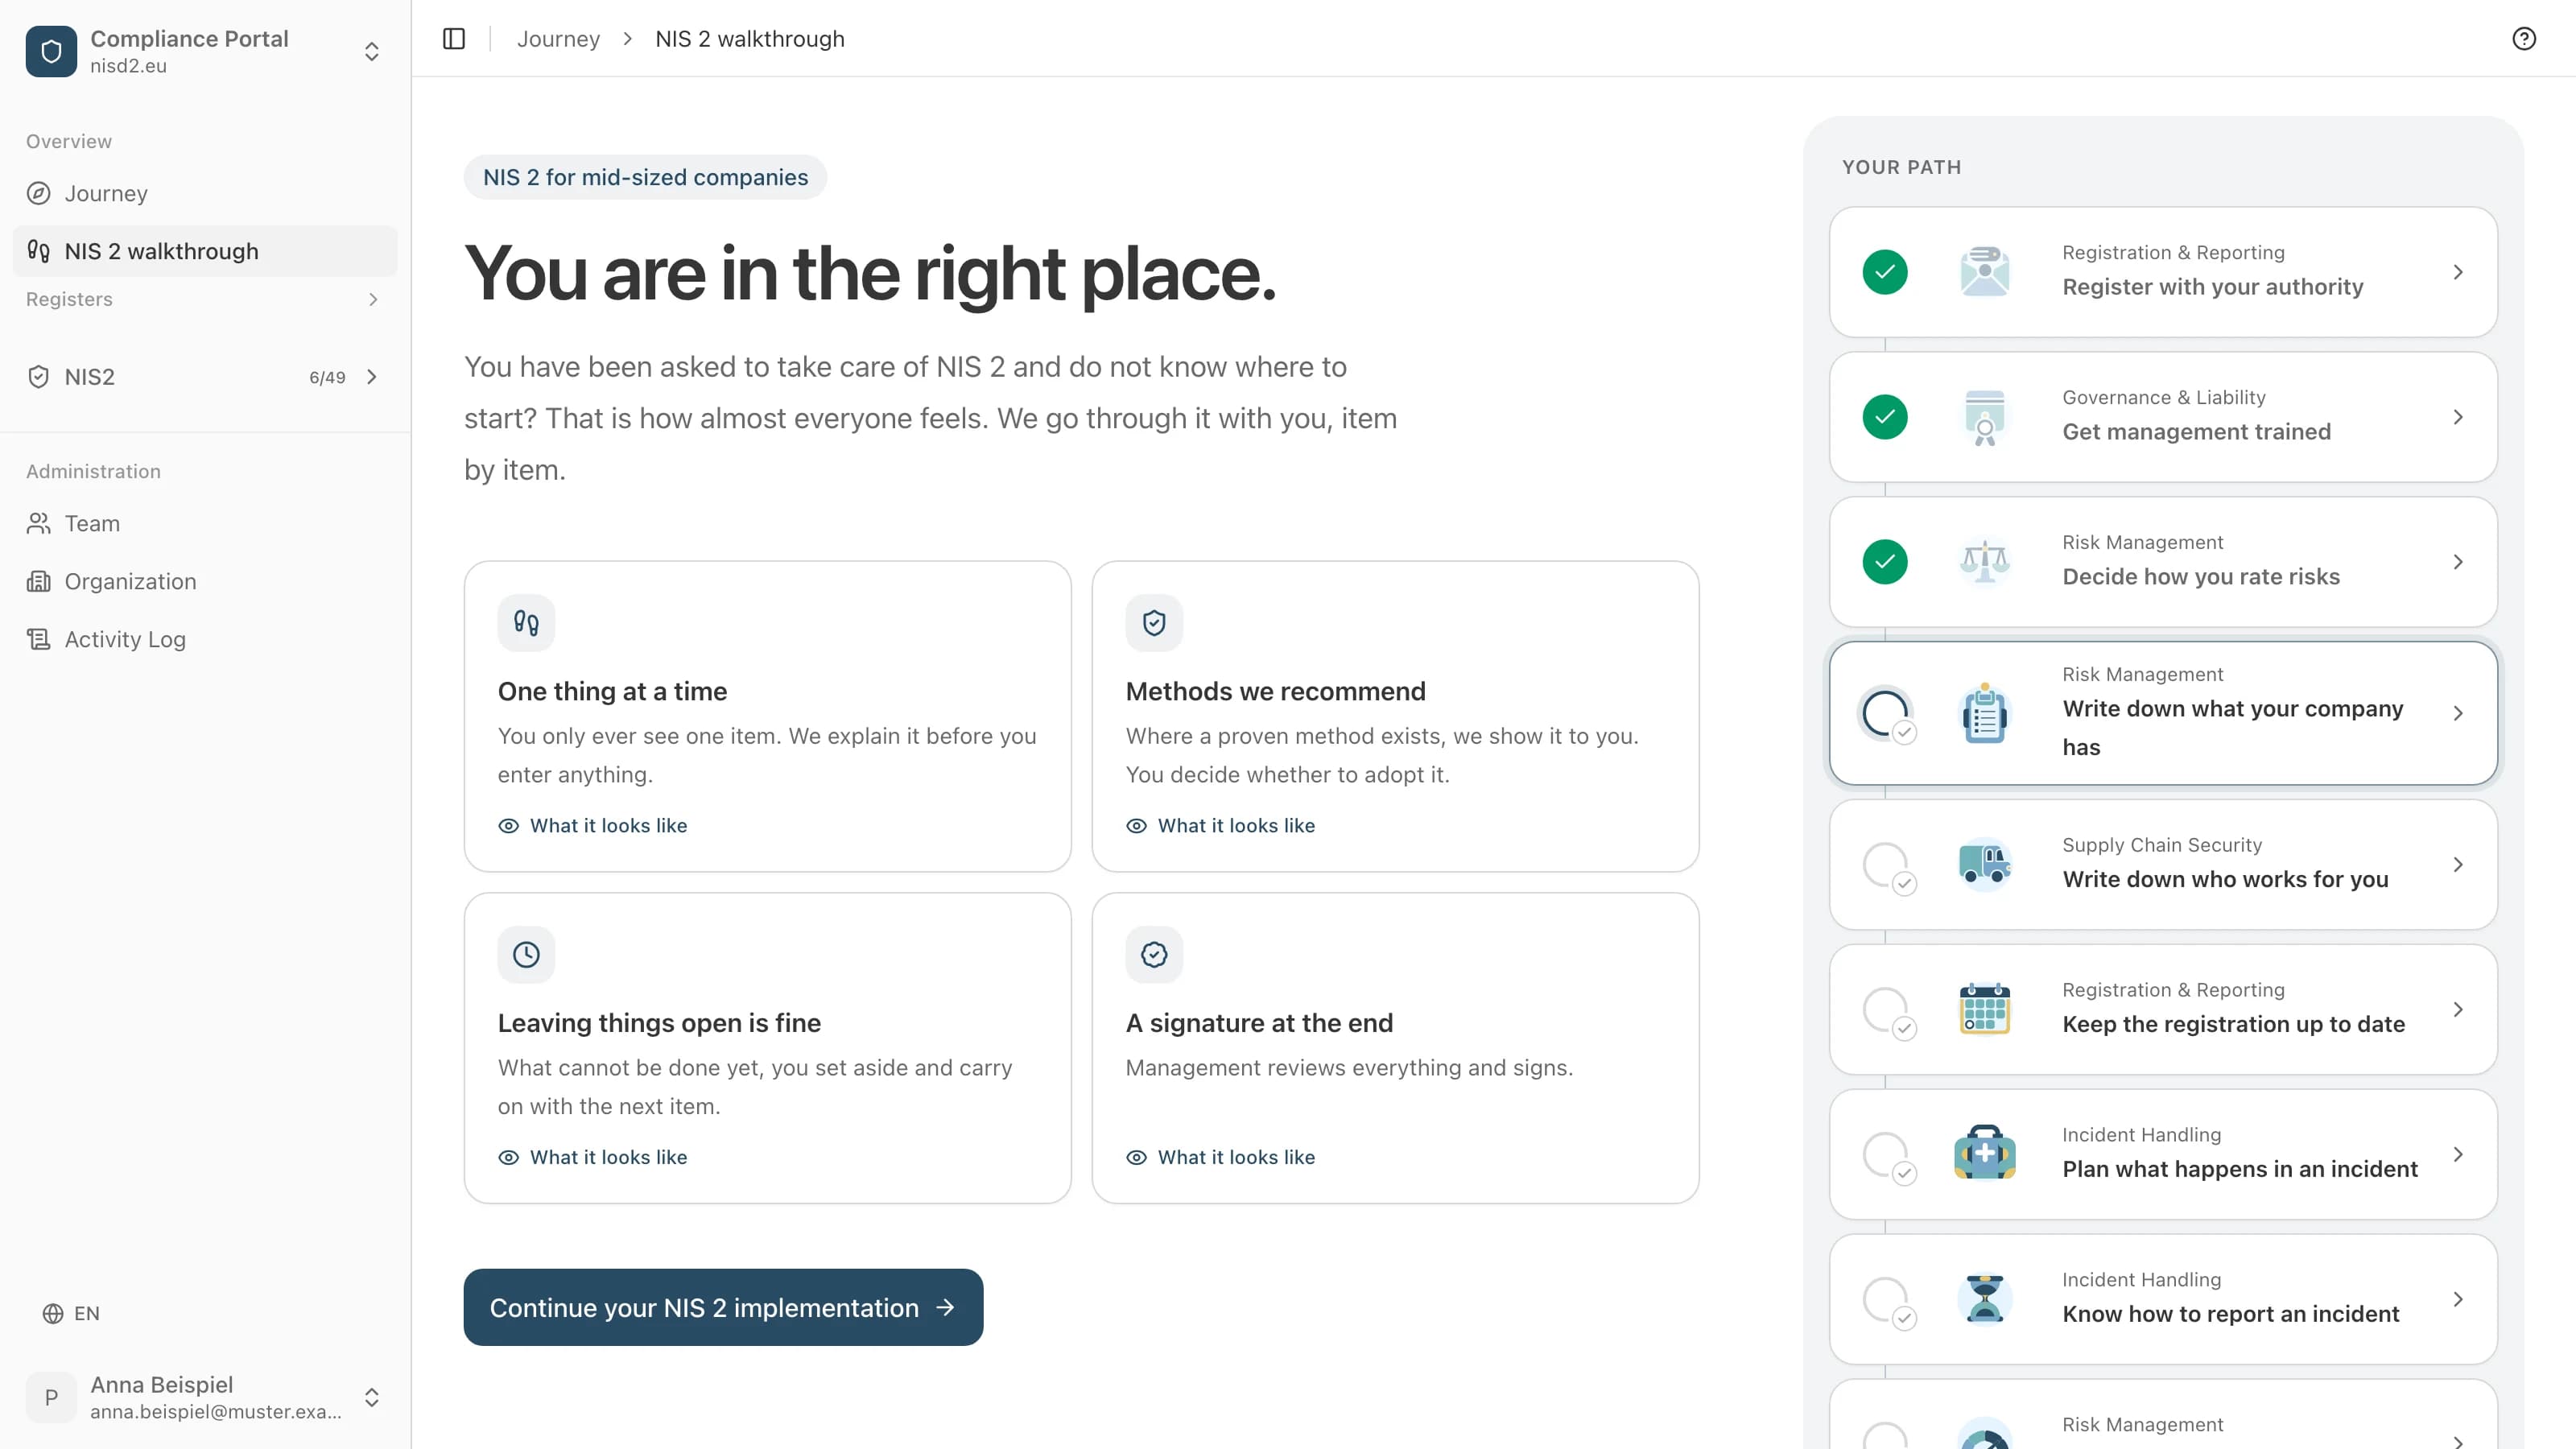
We build the NIS 2 walkthrough at nisd2.eu, software for doing it in-house: €4,800 net a year, or free on your own servers (open source, AGPL-3.0).
If a consultant fits better, we name one to three firms on request and write down why those. If an engagement follows, the firm pays us a commission, normally 15 percent of its net fee. You pay nothing for it, and your own consultant is just as fine.
What does a NIS 2 consultant cost?
For a gap assessment, German consultancies publish prices between €2,000 and €6,900, one-off and mostly as starting prices (cyberkom, ing-ism, Blackfort, DATAGROUP, and secunet, as of October 2026). For the whole project there is no honest flat figure, because it depends on your size and your starting point.
Do I have to hire a consultant for NIS 2?
No. The law requires measures, not consulting. Who implements them is left open. Responsibility for implementing and overseeing them stays with management (§ 38(1) BSIG, Art. 20(1) NIS 2).
- BSIG as amended by the NIS2UmsuCG: § 30(1), § 32, § 38(1) and (3); Directive (EU) 2022/2555, Art. 20, 21 and 23. gesetze-im-internet.de/bsig_2025
- Published prices for a NIS 2 gap assessment on the websites of cyberkom, ing-ism, Blackfort, DATAGROUP, and secunet, as of October 2026.
- Our referral terms, as of 30 August 2026. nisd2.eu/vermittlung
Been asked to handle NIS2?
In the end you have everything in one document: what is done, what is still open, and your management's approval with name and date. The texts are drafted from what you enter.